The Operator Calls Are Coming From Inside the Namespace
Kubernetes operators are supposed to make life easier. Give them cloud credentials, point them at your provider, and they’ll provision infrastructure for you. Config Connector, ACK, ASO, Crossplane — they all work the same way.
They also all have the same problem.
I spent six months hunting bugs in these operators. Most of them trust user-supplied references without checking if the user should actually have access to what they’re referencing. Create a custom resource pointing at someone else’s cloud resources, and the operator will happily modify them using its own credentials. Your RBAC says you can only touch your namespace. The operator’s service account can touch everything.
This talk covers what I found, how the attacks work, and what to check before you deploy operators in production. No slides full of vendor logos — just patterns I saw across four projects and the guardrails that would’ve stopped them.
Speaker
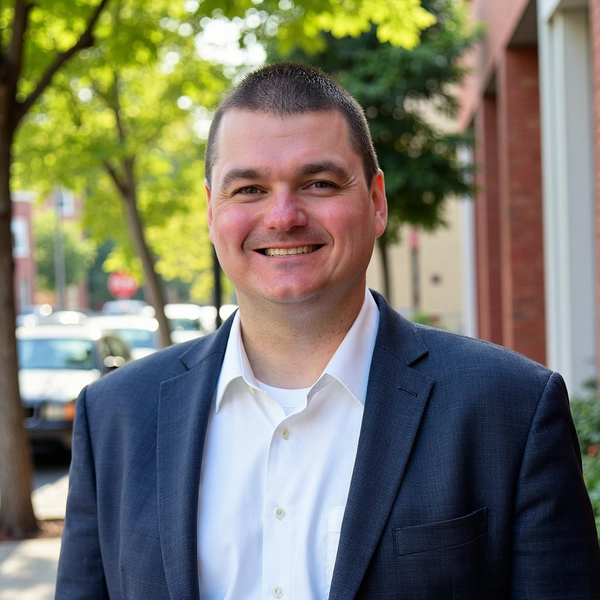
Justin O'leary
Justin O’Leary is a security researcher focused on cloud-native infrastructure vulnerabilities. His work on confused deputy flaws in Kubernetes operators has uncovered privilege escalation paths ...
Platinum Sponsors
Join as Platinum Sponsor!Gold Sponsors
Join as Gold Sponsor!
Silver Sponsors
Join as Silver Sponsor!Community Sponsors
Join as Community Sponsor!
Media Sponsors
Join as Media Sponsor!
À la carte Sponsors
Join as À la carte Sponsor!